Platform use cases

Automated Vulnerability Detection Platform for Post-Deployment Risk

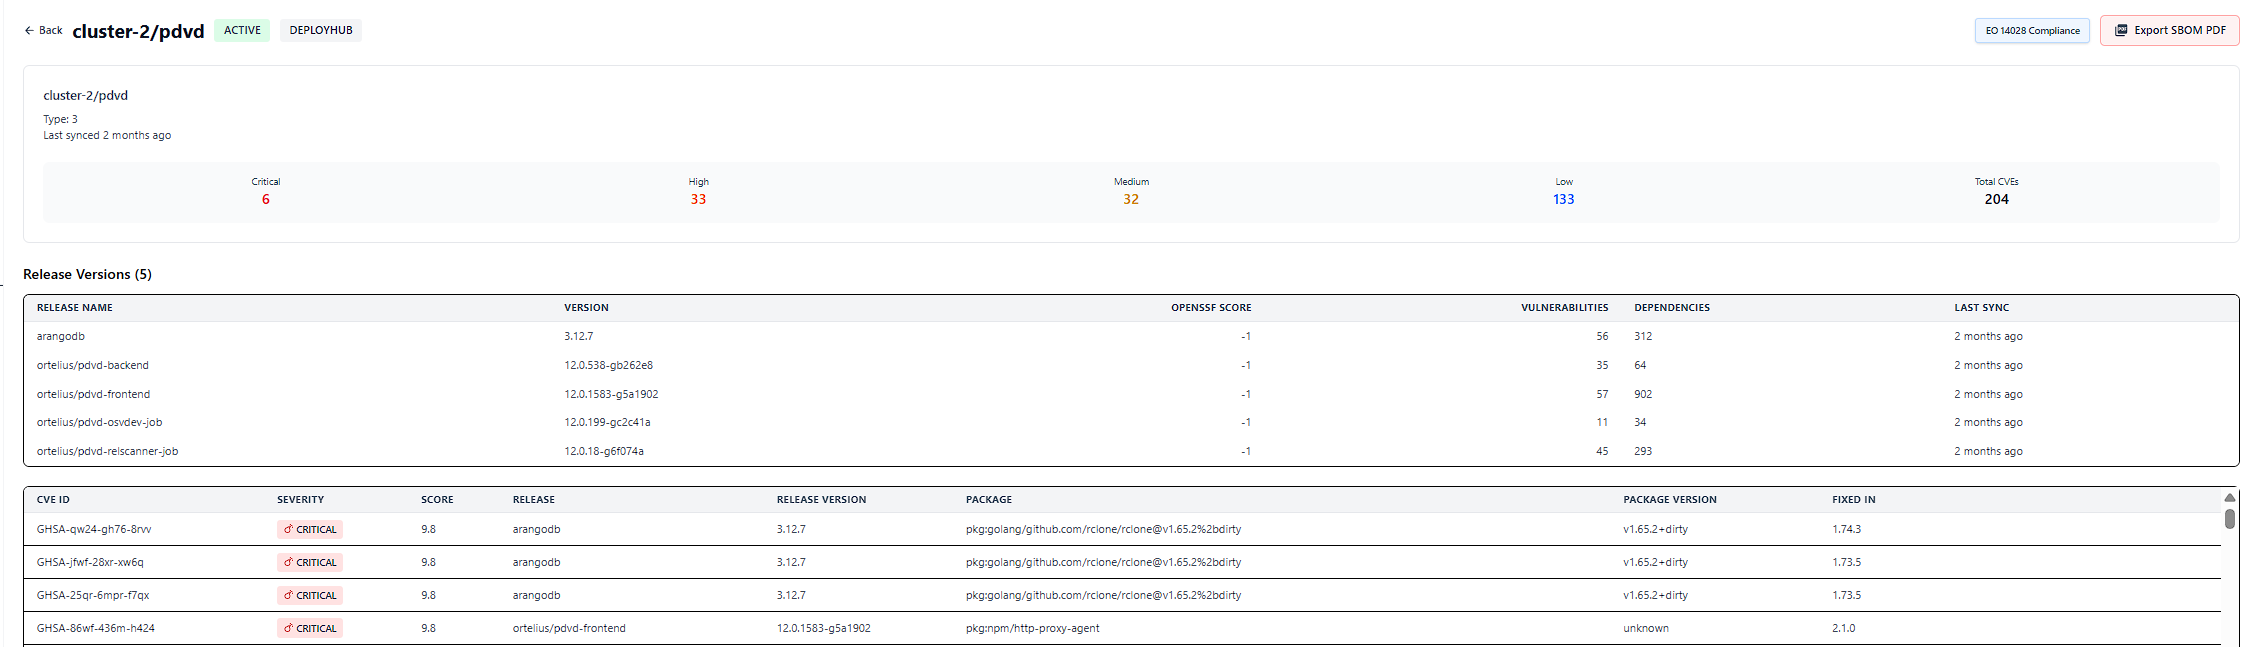
DeployHub is an automated vulnerability detection platform built to identify open-source vulnerabilities that affect software after deployment. With continuous post-deployment vulnerability detection, DeployHub correlates newly disclosed CVEs with the packages, applications, environments, and endpoints where vulnerable software is actually running.ย 

The Risk

Automated Vulnerability Detection Must Continue After Deployment

Open-source vulnerabilities do not stop appearing when software is released. New CVEs can be disclosed days, months, or years after deployment, leaving production systems exposed even when they passed every build-time security check.

A Continuous automated vulnerability detection platform gives security and DevOps teams an updated view of vulnerabilities affecting deployed software, so they can determine what is actually at risk instead of relying solely on pre-deployment scan results.

Platform Benefits

How DeployHub Delivers Automated Vulnerability Detection - Post Deployment

Our Automated Vulnerability Detection Platform continuously correlates newly disclosed vulnerabilities with the software already deployed across your environments. Unlike traditional scanners that primarily evaluate repositories, builds, or container images, DeployHub provides post-deployment vulnerability detection by mapping vulnerable package versions to the applications and endpoints where they are actually running.

This production context helps teams reduce vulnerability noise, understand blast radius, and prioritize remediation based on real exposure.

DeployHub Enables:

Continuous CVE Detection

Automatically correlate newly disclosed vulnerabilities against software already deployed in production.

SBOM-to-Endpoint Mapping

Map vulnerable packages and versions directly to the applications, environments, and endpoints where they are running.

Agentless Monitoring

Maintain continuous production visibility using SBOM intelligence and deployment evidence, without installing heavyweight endpoint agents.

CVE Blast-Radius Analysis

Immediately identify every application, service, cluster, and endpoint affected by a newly discovered vulnerability.

Production-First Prioritization

Reduce vulnerability noise by focusing remediation on vulnerabilities that are actually impacting deployed software.

Reduced CVE Noise for Focused Remediation

Focuses remediation on vulnerable components that are actually deployed instead of treating every dependency discovered during development as an active production threat.

Discover Which Vulnerabilities Impact Your Systems

Use the free DeployHub SaaS platform to detect and locate vulnerabilities across production environments, without waiting for budget approval or a lengthy procurement cycle.

Our free SaaS platform is based on Ortelius, an open-source project incubating at the Linux Foundation. No budget authority. No agents. No reason to wait.

Need Help?ย  Schedule a tech call with the DeployHub Team or chat with the Ortelius Community

Key Concept:ย 

Learn more about Automated Vulnerability Detection for Live Systems

Platform Comparison

Hereโ€™s how DeployHub compares to Traditional SCA, Scanners, and SAST.

Capability DeployHub Traditional SCA Container Scanners SAST
Maps CVEs to deployed applications Yes Limited Container-only No
Shows where vulnerable packages are running Yes No Limited No
Tracks ownership and blast radius Yes Limited Limited No
Uses SBOMs after deployment Yes Limited Limited No
Supports agentless operational visibility Yes Usually no Usually no No

Additional DeployHub Features

Detect

Know when a new CVE affects software you’ve already released by using your SBOM insights.

Learn more

Locate

See the exact package, version, artifact, and endpoint affected by a newly reported CVE.

Learn more

Defend

Continuously monitor your deployed software without agents or production rescanning.

Learn more

Measure Open-Source Project Risk With OpenSSF Scorecard

DeployHub aggregates OpenSSF Scorecard data to help teams evaluate the security practices of the open-source projects they depend on, not just whether those projects currently have known CVEs

Learn more

Make Your SBOMs Operational

Turn static SBOM files into a live inventory of the open-source packages and versions running across your software estate.

Learn more

Open Source at the Core

Built on Ortelius, DeployHub gives teams an open, extensible foundation for software inventory, SBOM intelligence, deployment tracking, and vulnerability defense.

Learn more

ortelius-stacked-color-small

meet ortelius

Explore the Open-Source Core Behind DeployHub

DeployHub is built on Ortelius, the open-source foundation for post-deployment vulnerability intelligence. Ortelius connects SBOMs, deployment data, applications, environments, and endpoints so teams of all sizes and budget constraints can determine whether newly disclosed vulnerabilities are actually affecting live systems.

Ortelius is an open-source project incubating at the Continuous Delivery Foundation.

Our Partners

catalyst campus
sda tap lab logo